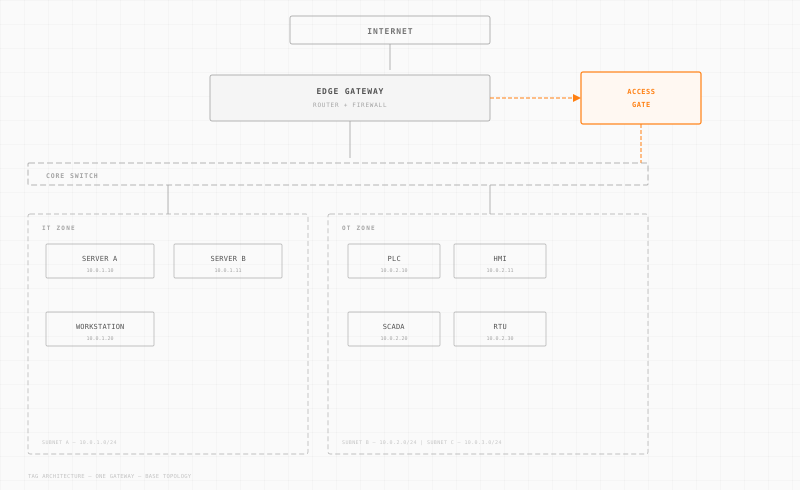
A CMMC Enduring Exception is, in the words of 32 CFR 170.4, "a special circumstance or system where remediation and full compliance with CMMC security requirements is not feasible", such as a PLC or CNC controller whose firmware cannot do MFA or write an audit log. It must be documented in the System Security Plan, and unlike a temporary deficiency tracked in a POA&M, it lasts for the life of the machine. It is not a waiver: each exception needs a compensating control that is running and produces evidence, as set out in the guide to CMMC exceptions and compensating controls for OT.
Back to Glossary
CMMC enduring exceptionCMMC complianceOT legacy systems
CMMC Enduring Exception
1 min read
Other Terms
CMMC shared responsibility matrixCMMC compliance
CMMC Shared Responsibility Matrix
A CMMC shared responsibility matrix maps every NIST 800-171 control to the party that enforces it, separating what a security tool handles, what the customer owns, and what needs compensating controls for OT assets.
CUI enclaveCMMC compliance
CUI Enclave
A CUI enclave is an isolated network segment holding every system that stores, processes, or transmits Controlled Unclassified Information, enforced by identity-based access rather than simple network separation.
Third-party remote accessVendor access
Acceso remoto de terceros
El acceso remoto de terceros es la conectividad que se concede a proveedores, integradores y contratistas externos para que mantengan o den soporte a tus sistemas desde fuera de las instalaciones. Es una de las vías de brecha más comunes, por lo que necesita un acceso intermediado, con privilegios mínimos y registrado en lugar de una cuenta de VPN compartida.