Secure MAVLink across your UAV fleet. No autopilot firmware changes.
MAVLink was built for serial links. It now runs over WiFi, cellular and satellite, in cleartext. This guide shows how to encrypt and authorize it from end to end.
Last updated:
Built for trusted serial links
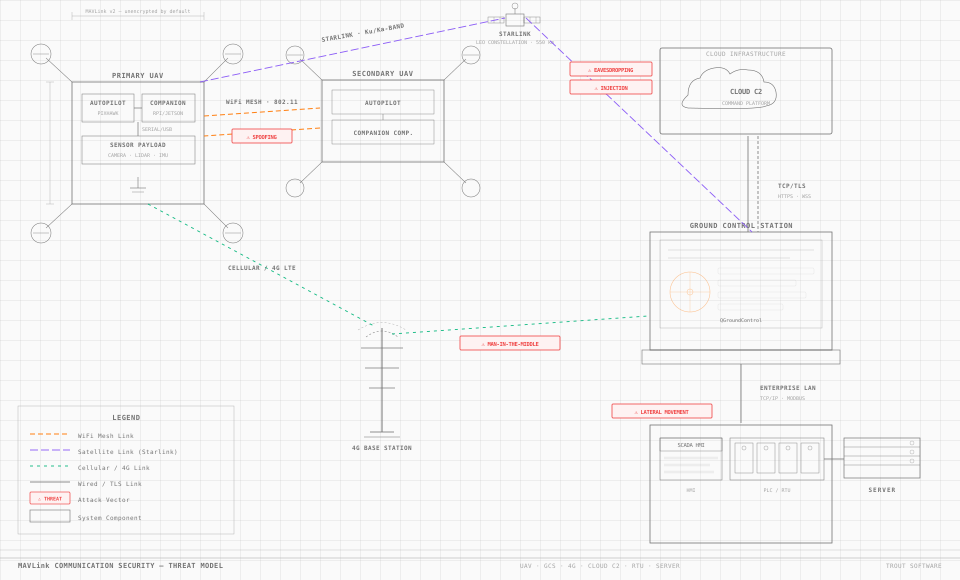
MAVLink was designed in 2009 for point-to-point serial connections between a single autopilot and a ground station. It assumed a trusted, physically isolated link. That assumption collapses when UAVs communicate over WiFi, 4G, and satellite: links that traverse public infrastructure.
Telemetry and commands travel in cleartext
MAVLink v1 and v2 transmit GPS coordinates, altitude, heading, battery state, and control commands in plaintext. Any device on the radio link or network path can read every packet. Message signing in v2 authenticates the payload, but does not encrypt it.
Shared secrets without rotation
MAVLink v2 signing uses a single shared passphrase across all participants. There is no key rotation mechanism, no forward secrecy, no per-session keys. Compromise of one node exposes the signing capability for the entire fleet.
Command injection with off-the-shelf radios
The barrier to entry is low and asymmetric. A receive-only SDR that costs about $30 (an RTL-SDR) is enough to eavesdrop on cleartext telemetry and read GPS, heading, and mission data off the air. Injecting commands takes more: a transmit-capable SDR such as a HackRF or bladeRF, roughly $150 and up. Once an attacker can transmit, SET_MODE, DO_SET_HOME, and MISSION_ITEM are legitimate protocol commands that need no exploit. The autopilot has no way to tell an authorized sender from an unauthorized one.
Four kinds of MAVLink attack.
MAVLink threats span confidentiality, integrity, availability, and safety. Each category exploits the protocol's native trust model, and each has direct physical consequences when the target is an airborne vehicle.

Confidentiality
Telemetry broadcasts GPS position, altitude, heading, and sensor data in cleartext. An attacker can track vehicle location, infer mission objectives, and intercept sensor feeds without transmitting a single packet.
Integrity
Forged MAVLink packets can alter waypoints, change flight modes, or override geofence boundaries. GPS spoofing via replayed GLOBAL_POSITION_INT messages can divert vehicles to unauthorized locations.
Availability
Flooding the MAVLink serial bus or radio channel with high-rate messages causes message drops and communication timeouts. The vehicle enters failsafe mode, potentially triggering an uncontrolled landing in hostile terrain.
Safety
PARAM_SET commands can modify altitude limits, maximum velocity, or battery failsafe thresholds. These changes persist across reboots. A compromised parameter set can cause a vehicle to operate outside its safe flight envelope.
A zero-trust overlay for MAVLink.
Each vehicle is encrypted, verified and authorized.
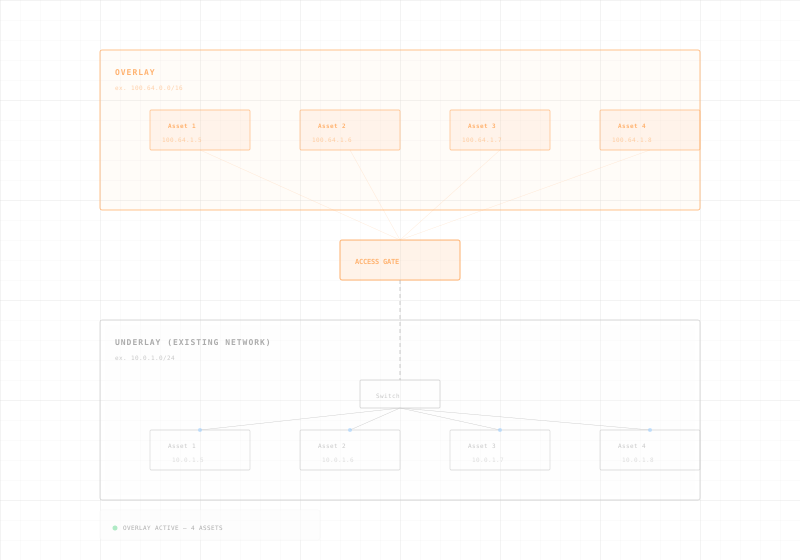
A WireGuard agent on each vehicle's companion computer establishes an encrypted tunnel to the Access Gate. MAVLink traffic is encapsulated before it reaches the radio link. The autopilot continues to speak standard MAVLink over its local serial connection. No firmware changes, no protocol modifications.
The Access Gate terminates the tunnel, verifies the vehicle's cryptographic identity, applies command authorization policies, and logs every message. Only authorized commands reach the ground control station or cloud C2 platform.

Vehicle identity
Each UAV holds a unique cryptographic identity (WireGuard keypair). No shared secrets, no passphrase-based signing. Compromise of one vehicle does not affect the fleet.
Continuous verification
Every MAVLink message traverses the encrypted tunnel. The Access Gate verifies the source identity on every packet, not just at session establishment.
Micro-segmentation
Each vehicle communicates only with its authorized ground station or C2 endpoint. Lateral movement between vehicles is blocked by default. Fleet-wide compromise requires compromising every tunnel independently.
End-to-end encryption
WireGuard provides authenticated encryption (ChaCha20-Poly1305) with perfect forward secrecy. Telemetry, commands, and sensor data are encrypted from companion computer to Access Gate.
Full audit trail
Every MAVLink command, telemetry message, and parameter change is logged with vehicle identity and timestamp. You can reconstruct any incident in full.
Download the full MAVLink security guide.
Get the complete 31-page guide: MAVLink protocol architecture, threat taxonomy, cryptographic remediation approaches, zero-trust overlay design, implementation roadmap, and regulatory compliance mapping.
What you'll learn
Why MAVLink has no native encryption and why message signing is insufficient. How the four attack categories, eavesdropping, injection, denial of service, and parameter manipulation, translate to physical consequences. How a WireGuard overlay provides end-to-end encryption without modifying autopilot firmware.
Deploy with Access Gate
Access Gate implements the zero-trust overlay as a single on-premise appliance. WireGuard tunnel termination, vehicle identity verification, command authorization, and full audit logging. No changes to autopilots, no cloud dependency, works over any link type.
Common questions about securing MAVLink.
Zero-trust pillars: vehicle identity, continuous verification, micro-segmentation, end-to-end encryption, and full audit. Applied without modifying a single autopilot.
MAVLink was designed for direct serial connections between an autopilot and a ground station. It transmits system IDs, component IDs, and command payloads in cleartext with no authentication. MAVLink v2 added optional message signing, but it uses a shared secret with no key rotation, no forward secrecy, and no encryption of the payload itself. Any device that knows the passphrase can sign messages.
There are four primary categories. Confidentiality attacks eavesdrop on telemetry, GPS coordinates and sensor feeds. Integrity attacks inject commands and spoof GPS with forged MAVLink packets. Availability attacks flood the serial bus or radio link to cause denial of service. Safety attacks change flight parameters, such as altitude limits or geofence boundaries, to cause physical harm.
Yes. A WireGuard agent running on the companion computer (Raspberry Pi, Jetson) establishes an encrypted tunnel to the Access Gate. MAVLink traffic is encapsulated inside this tunnel before it leaves the vehicle. The autopilot continues to speak standard MAVLink over its serial connection to the companion computer. No firmware changes required.
WireGuard adds a small overhead per packet, on the order of 1 to 3 ms on a typical companion computer (Raspberry Pi or Jetson class). At standard MAVLink telemetry rates of 1 to 10 Hz, that is comfortably within bounds. Measure the exact added latency and jitter on your own airframe rather than assume it. Real-time control that needs sub-millisecond timing stays on the local serial bus between autopilot and companion computer. Only the long-haul link is encrypted, so the flight loop never waits on the tunnel.
It helps with both. FAA BVLOS waivers increasingly require proof of command-and-control link security. CMMC Level 2 requires encryption of CUI in transit, and telemetry from defense-related UAV operations can qualify as CUI. The zero-trust overlay provides encryption, identity verification, command authorization, and full audit logging for both.