Secure every airport, rail line and port. Certified systems stay untouched.
Transportation cybersecurity for OT
Control who reaches baggage, signaling and port systems. Nothing is installed on them, so nothing needs requalification.
Last updated:

Secure airport systems.
Protect BHS, BMS, FIDS and access control without requalification.
Learn more
Secure rail signaling.
Control who reaches signaling, SCADA and train control. Nothing to install on certified equipment.
Learn more
Secure ports and terminals.
Control who reaches cranes, container systems and logistics networks.
Learn moreControl access without requalification.
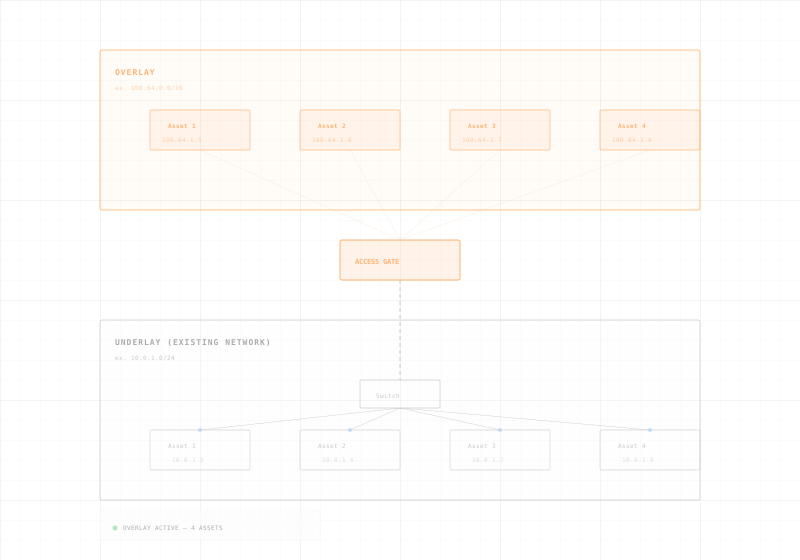
Access Gate connects to your existing network. Certified systems stay as they are.
See every machine.
Find every machine across terminals, stations, depots and ports.
Control who reaches what.
Keep office traffic away from BHS, signaling and port control. No VLAN changes.
Reach any machine, securely.
OEMs and contractors log in with MFA. Their VPN or 4G link ends at the gate.
Prove every audit.
Every connection is logged. Export audit evidence on demand.

Up in a day, no requalification.
Access Gate connects to your existing network. Certified BHS, signaling and SCADA stay unchanged.
Nothing to install on certified machines.
Access Gate works from the network. Safety certifications and type approvals stay intact.
New controls for old systems.
Add MFA and audit logs to air-gapped transport systems without replacing them.
The gate is the first service you run, not the last.
Secure your plants today. Control your digitalization tomorrow.
Access Gate puts compute on the wire, next to your assets. Once the gate is in, the same box hosts the services that pull OT in securely: remote access, protocol gateways, DNS and time, historian, update server. Accelerate your digitalization, in control.
Trusted by transportation and critical infrastructure operators.

distributed sites protected across harsh operational environments, securing critical infrastructure without agents or downtime.
Trusted by leading companies


“Our BHS was certified five years ago and we couldn't risk requalification. Trout gave us a path to bring services to legacy environments without requalification.”
CISO
Airport Operations · European Airport Operator
Common questions about transportation security.
requalification events triggered by deployment, the Access Gate never touches certified operational equipment.
No. The Access Gate operates at the network level, it never installs agents, modifies configurations, or touches certified endpoints. BHS controllers, rail interlocking systems, and port SCADA remain exactly as certified. No re-certification or requalification required.
Yes. The Access Gate brings modern security services, zero-trust access, MFA, session logging, and micro-segmentation, to air-gapped and legacy OT networks. It operates entirely on-premise with zero cloud dependency, so isolated systems stay isolated.
The Access Gate creates encrypted overlay networks across all sites, terminals, stations, depots, and port facilities, with overlay micro-segmentation between corporate IT and operational networks. Policy is managed centrally and enforced consistently at every location, including remote or unmanned sites.
The Access Gate supports IEC 62443 for industrial security, NIST SP 800-82 for OT, and sector-specific directives for rail, aviation, and maritime. It generates assessment-ready documentation and provides continuous control enforcement.
The built-in bastion host provides a controlled gateway for equipment OEMs, maintenance contractors, and third-party integrators. Each session requires MFA, is scoped to specific systems, time-limited, and fully recorded. The VPN or 4G link ends at the gate, with no direct route into operational networks.
Yes. The Access Gate connects to existing network infrastructure rather than cutting into it with zero downtime. No re-cabling, no IP changes, no service interruption. Deployment happens during normal operations, no maintenance windows or service outages required.