
Vendors reach one machine, and every session is recorded.
Secure remote access for OT means a vendor or engineer reaches one machine, for one task, for a set time. The session is recorded. Access Gate does this on your site, on top of your existing VPN or 4G link.
Last updated:


Why remote access is hard to audit
Vendors connect to the plant through a VPN, a jump server or a shared account. Through a VPN, a vendor session can reach every machine on the subnet behind the tunnel. VPN logs record the tunnel connection, without the commands sent or the person behind a shared account.
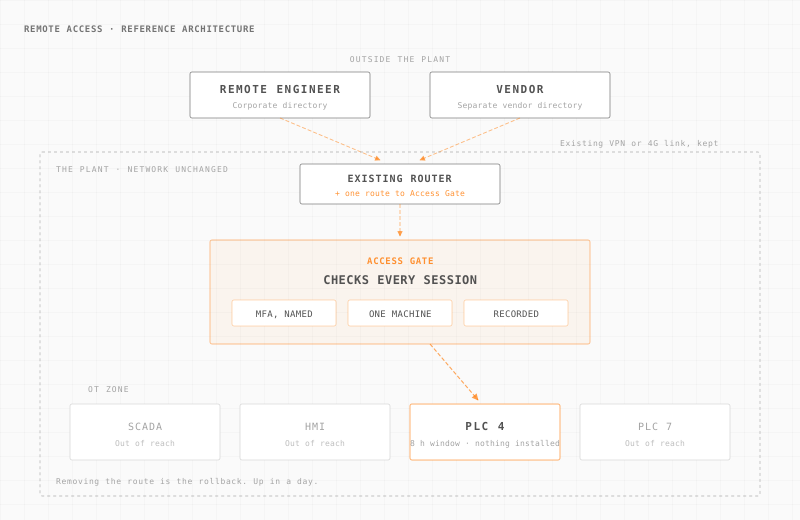
How a session reaches a machine.
The vendor keeps the VPN or 4G link they already use. That link ends at Access Gate. Access Gate then runs three checks.
The user signs in at the gate.
Users sign in through a browser with MFA. Staff use your corporate directory, and vendors use a separate one. The vendor installs no client.
The session reaches one machine.
One authorized machine, over one authorized protocol. The user never gets an IP address on your network.
Access closes when the window ends.
Access opens for 15 minutes, 1 hour, 8 hours or a set maintenance window. No standing account stays open.
What every session records.
Every session passes through Access Gate. Access Gate records each session while it runs, and the recording stays on site.
Who.
A named person on every session.
- Named user, staff or vendor
- Directory and MFA used
- Access agreement, with timestamp
- Time window granted
What.
The machine, the protocol and the actions.
- Target machine
- SSH, RDP, VNC, HTTP, Modbus, OPC UA
- Commands and screens
- Actions allowed and blocked
Replay.
A recording you can play back.
- SSH terminal input and output
- RDP screen activity
- Every HTTP request
- Indexed and kept on site
Where Access Gate sits on the network.
One route on the existing router sends remote traffic to Access Gate. Access Gate applies one rule per user and per machine. Other machines are unreachable from the session.
Machines come from the inventory.
You assign each vendor machines from the asset inventory. The vendor reaches only those.
OT asset inventoryEvery user has a name.
Staff sign in with Active Directory or Entra ID. Vendors use a second directory or the one built into Access Gate.
OT identity and MFASession records for audits.
Each record lists the user, the machine, the time and the recording. It is the audit trail for an assessment or an incident.
OT complianceHow each remote access option controls a session.
Five common ways to give a vendor access, by where the user is checked, what the session reaches and what is kept.
| Option | Where the user is checked | What a session reaches | Record of the session |
|---|---|---|---|
| VPN | OnceOnce, when the tunnel opens. | Whole subnetThe whole subnet behind the tunnel. | Logs onlyConnection logs only. |
| Jump server or bastion | At the hostAt the jump host. The last hop can use a shared local account. | WideWhatever the host can reach. A direct route to the PLC stays open until the network is segmented. | If enabledHost logs, if enabled. |
| Vendor portal (cloud broker such as Talk2M or IXON Cloud) | Their cloudIn the vendor's cloud. | Machine LANThe machine LAN over a VPN, or a registered device. | VariesConnection logs. Session detail varies by plan. |
| ZTNA gateway | At the edgeAt the network entry. | Remote onlyRemote access only. Local access on the plant floor is not covered. | VariesVaries. Several products do not document session replay. |
| Access GateTrout Access Gate | Per sessionIn front of the machine, on every session, with MFA. | One machineOne machine, over one protocol. | ReplayA full recording you can replay, kept on site. |
What the frameworks ask of remote access.
The frameworks below require strong authentication on remote access and a record tied to a named user. Access Gate covers these requirements without changes to the machines.
| Framework | Requirement | What Access Gate gives you |
|---|---|---|
| IEC 62443-3-3 SR 1.1 and SR 1.13 | Identify and authenticate human users. Monitor and control all access through untrusted networks. | The VPN or 4G link ends at the gate, and each user is authenticated before reaching a machine. |
| NIST SP 800-82 | Treat remote access into an ICS as a path that needs strong authentication and monitoring. | MFA on every session and a recording of what was done. |
| CMMC Level 2 / NIST SP 800-171 3.1.12, 3.1.14, 3.5.3 | Monitor and control remote sessions through managed access points, with MFA on network access. | Every session passes the gate, with MFA, even for PLCs and HMIs that cannot ask for a second factor. |
| NERC CIP-005-7 R2 | Route Interactive Remote Access through an Intermediate System with MFA, and be able to end active vendor sessions. | Access Gate is the Intermediate System. It lists active vendor sessions, and you can end any of them. |
How do you secure OT remote access?
Five steps that work with or without Access Gate. For an outside company, the guide shows how to give a vendor access to one machine.
- 01
List every way in.
Include the VPN, the jump server, any vendor 4G router in a cabinet and any remaining modem. Check the cabinets for routers and modems missing from the network diagram.
- 02
Put the gate beside the network.
Connect Access Gate and add one route on your existing router. Removing the route is the rollback. Each site is up in a day, and took 4 hours per site at Thales.
- 03
Connect your directories.
Staff use Active Directory or Entra ID. Vendors use a second directory or the one built into Access Gate. MFA runs at the gate, and TOTP works offline.
- 04
Give each vendor one machine.
Pick the machine, the protocol and the time window. Ask for an access agreement before each session starts.
- 05
Close the old paths.
Once sessions run through Access Gate, remove the VPN routes that still reach the machines. Access Gate is then the only remote path to those machines.
Remote access is part of the Access Gate subscription: hardware, software, updates and support, with no per-seat fees.
Questions about secure remote access for OT.
Agents installed on your PLCs, HMIs or SCADA servers. Access Gate controls each session in front of the machine.
It is how engineers, integrators and equipment vendors reach PLCs, HMIs and SCADA servers from outside the site. The VPN or 4G link only carries the connection. Access Gate sits in front of the machines and checks each user with MFA. Each session reaches one machine over one protocol, is recorded and closes on time.
They keep the VPN or 4G link they already use, and that link ends at the gate. They open a browser and sign in with MFA. The gate connects them to the authorized machine at the application layer, and they never get an IP address on your network. Engineers who support distant plants work the same way, with their usual identity.
HTTP and HTTPS, SSH, RDP, VNC, Modbus TCP and OPC UA, inspected at the application layer. You can allow a protocol and limit what it may do. For example, allow SSH but block specific commands, or allow HTTP GET but deny POST.
Yes. Access Gate runs fully on your site, with no cloud. Proxying, recording and policy all happen locally, which suits ITAR, CMMC and air-gapped sites. TOTP works offline. If the appliance itself is offline, the network keeps running and operators keep control at their local panels.
Access Gate is an all-inclusive annual subscription covering hardware, software, updates and support, with no per-seat fees. Access Gate IDMZ Small is for small and mid-size sites and starts at $5,745 a year per site. Access Gate IDMZ Large covers plants, control centers and large estates. Current list prices are on the pricing page.
No. The same appliance controls who reaches which machine inside the plant, enforces MFA and keeps a tamper-evident audit trail. You can bring internal flows under control first, then open remote access onto a controlled network. A large manufacturer in North Carolina manages 1,300 assets and 660 users with Access Gate.
CISA guidance for critical infrastructure asks for phishing-resistant MFA on every remote connection. It also asks for least-privilege access, no single-factor exposure of OT to the internet, and logs detailed enough to rebuild a session. A PLC or an RTU cannot ask for a second factor, so Access Gate runs the check in front of it. The machine's own communication is unchanged.
See a recorded session
Watch a vendor session, then replay it.
An engineer shows you a session to one machine, its recording and its replay, on a network like yours.