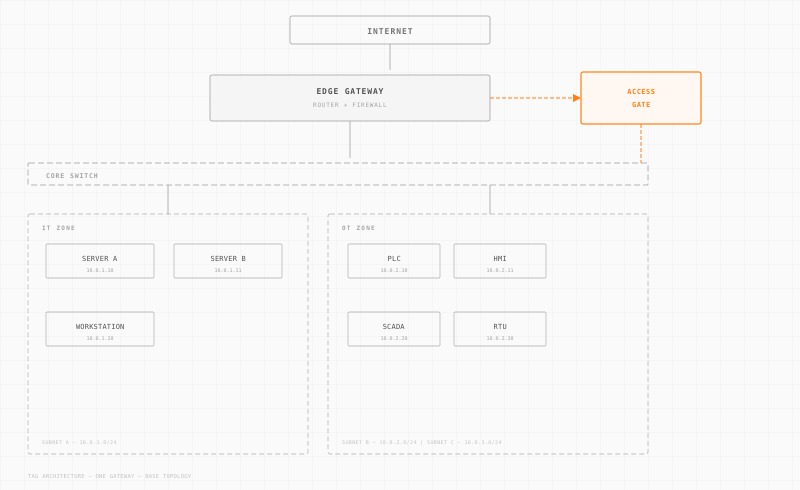
Access Gate datasheet. All the specs on two pages.
Deployment modes, supported protocols, throughput, compliance coverage and integration requirements for Trout Access Gates. Written for IT and OT teams.
Last updated:
What Access Gate does.
Access Gate connects to your existing network as a Trout appliance. No recabling, no IP changes, nothing to install on machines. It builds a Zero Trust overlay that authenticates, inspects and logs every connection, session by session.
Zero Trust inside the LAN.
Applies identity-based controls to internal traffic, not just the perimeter.
Works with your existing gateways.
Connects to current edge or OT gateways without redesigning the network.
Protects only the flows that matter.
Selected flows are routed through enforcement while normal traffic stays unchanged.
Rolls out step by step.
Introduce Zero Trust step by step without disrupting operations.

What's inside.
The TAG 2026 datasheet covers hardware specs, deployment architectures, supported protocols, compliance mapping and integration requirements. It is written for security architects, network engineers and procurement teams.
Hardware specifications.
Form factor, interface count, throughput, power consumption, operating temperature range, and rack-mount specifications for both models.
Deployment architectures.
One Gateway, Two Gateway Layers, and Multi-Site deployment modes with traffic flow diagrams for north-south and east-west enforcement.
Supported protocols.
Full list of IT and OT protocols supported for deep inspection: Modbus, DNP3, IEC 61850, OPC-UA, S7, BACnet, SSH, RDP, VNC, and more.
Compliance coverage.
CMMC 2.0, IEC 62443, NIST SP 800-82, and DoD Zero Trust pillars, with per-control mapping tables.
Download the TAG datasheet 2026.
Full technical specifications, deployment architectures, protocol support, and compliance mapping for the Trout Access Gate.
For security architects.
The datasheet includes traffic flow diagrams for all three deployment architectures, integration points with existing firewall and switch infrastructure, and per-protocol inspection capabilities.
Request a technical demo.
See the Access Gate live in a lab environment. We walk through deployment, policy configuration, session logging, and protocol inspection on real OT traffic.
Common questions about Access Gate.
agents required. Access Gate enforces Zero Trust at the network layer. Nothing to install on machines.
Access Gate Essential is a 1/2U rack-mount appliance. Access Gate Performance is a 1U rack-mount appliance. Both are designed for standard 19-inch rack installation. Detailed dimensions, weight, and interface specifications are in the datasheet.
Access Gate performs deep packet inspection for Modbus TCP/RTU, DNP3, IEC 61850 (GOOSE/MMS), OPC-UA, Siemens S7, BACnet and EtherNet/IP. Standard IT protocols (SSH, RDP, VNC, HTTPS, SMB) are also fully inspected. The complete protocol list is in the datasheet.
Throughput depends on the model and the deployment mode. The datasheet gives figures for north-south enforcement and east-west overlay enforcement. Industrial protocols use little bandwidth, so OT deployments usually run well within rated throughput.
No. The Access Gate is fully air-gap capable. All policy enforcement, session logging, and configuration management operates on-premise without any cloud connectivity. This makes it suitable for classified environments and isolated OT networks.
The Access Gate ships with a local web management interface accessible from the LAN. For multi-site deployments, a management plane can be established between Access Gates over the inter-site tunnel. No cloud portal or external management dependency is required.