Secure every vessel, even when comms are jammed.
Naval cybersecurity for OT
Control who reaches every system on crewed ships and uncrewed vessels. Rules keep running on board, with no cloud.
Last updated:
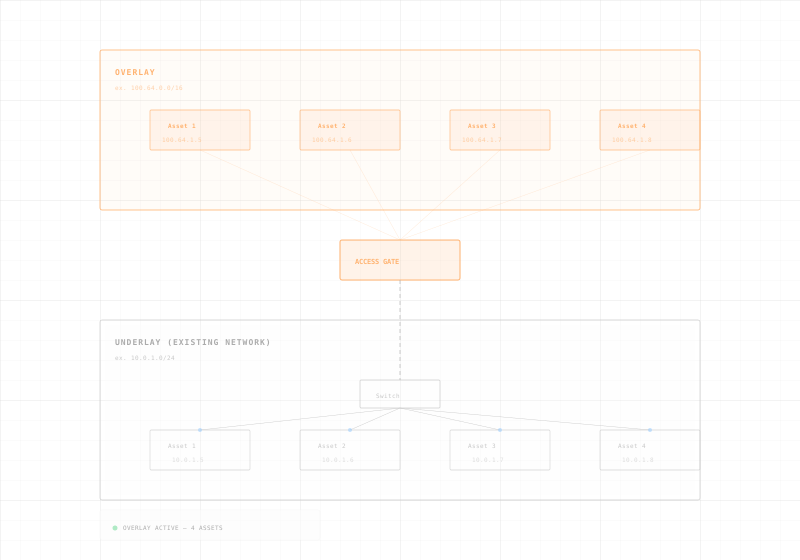
One gate per vessel. Four jobs.
Access Gate connects to the ship's existing network. Operations keep running.
See every machine.
Find every system on the ship network, from combat management to navigation.
Control who reaches what.
Crewed ships and USVs each reach only what they need. One compromised USV stays contained.
Reach any machine, securely.
Shore teams and allied partners log in with MFA. Each session is scoped, time-limited and logged.
Prove every audit.
Every connection is logged on board. Export the evidence your auditors ask for.

The gate is the first service you run, not the last.
Secure your plants today. Control your digitalization tomorrow.
Access Gate puts compute on the wire, next to your assets. Once the gate is in, the same box hosts the services that pull OT in securely: remote access, protocol gateways, DNS and time, historian, update server. Accelerate your digitalization, in control.
Trusted by defense forces and sovereign programs.

per site at Thales, from unboxing to running, in restricted on-premise networks.
Trusted by leading companies


“As we integrate autonomous platforms into the fleet, connectivity becomes both an enabler and a threat surface. Trout gives us Zero Trust enforcement at the fabric level.”
Cyber Operations Lead
Navy · European Navy
Download the DoD Zero Trust OT alignment.
How Access Gate maps to the seven pillars of the DoD Zero Trust Reference Architecture for naval and maritime OT.
What's inside.
DTM 25-003 alignment, the seven Zero Trust pillars mapped to Access Gate, OT deployment guidance and audit evidence for naval programs.
See it in action.
Book a live demo. See Access Gate connect to your network without rewiring or downtime.
Common questions about naval network security.
cloud dependencies. Access Gate runs on its own on board: sovereign, inspectable and built for air-gapped networks.
The Access Gate enforces Zero Trust policies autonomously on each vessel. It does not require reach-back to shore-based or cloud infrastructure. When connectivity is jammed, degraded, or denied, all policies continue enforcing locally. When comms are restored, logs and state synchronize automatically.
The Access Gate creates identity-aware micro-segmentation between crewed warships and autonomous surface vehicles. Each platform, manned or unmanned, gets independent network policies enforced at the device level. Compromising one USV cannot grant lateral access to ship C2 systems.
Yes. The Access Gate is fully on-premise with zero cloud dependency. All software is inspectable. All data and policies remain under national control. It deploys in air-gapped, classified, and ITAR-restricted environments, suitable for NATO and allied naval programs.
The Access Gate connects to the ship's existing network in a day. No re-cabling, no IP changes, no modifications to existing combat management or navigation systems. Operational from unboxing without infrastructure redesign.
Yes. The Access Gate enforces granular access policies per nation, role, and classification level. Allied partners can be granted controlled, time-limited, audited access to specific systems without exposing the broader fleet network.