
CMMC compliance for defense manufacturers
CMMC compliance for your OT systems.
Watch how Access Gate protects CUI on your machines (40 seconds).
CUI on shop-floor machines
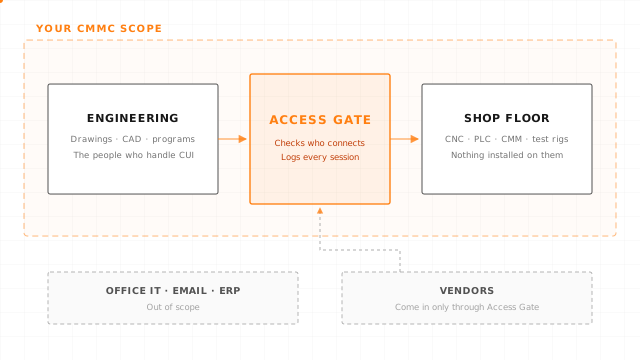
CUI has to reach shop-floor systems to make parts, print drawings and scan results. CMMC calls these OT systems specialized assets. They are hard to secure, and you must document how you protect them. Access Gate deploys ready-made protection, with the documentation that proves your compliance.
What Access Gate covers for CMMC Level 2.
These are the technical controls Access Gate handles on the machines your IT tools cannot reach.
- Access control (AC)
- Only named people reach each machine.
- Authentication (IA)
- MFA applies even on old machines.
- Audit (AU)
- Every session is logged.
- Network protection (SC)
- CUI machines are kept apart from the rest of the network.
- Assessment scope
- Only the enclave is in scope.
CUI Vault by NtelSec keeps your CUI in a managed Microsoft GCC High enclave. Access Gate carries it to the machines on your floor. Read the announcement
· Plants already running it

100%
of CUI data flows secured, for CMMC Level 2
“Trout has been outstanding across the board, from the quality of their product to the responsiveness of their team. They've been a true partner in helping us meet our CMMC goals.”

3 days
to CMMC Level 1, on site
“Access Gate makes overlay configuration feel approachable rather than specialist. The UI is intuitive and guides users through defining assets, services and access paths without requiring them to redesign the underlying network.”
Choose the Access Gate CMMC that fits your site.
One price per site, per year. It includes the appliance, the CMMC Edition, updates and support.

Small
Access Gate CMMC
$8,740 per site, per year
It fits a small plant or a single shop floor.
- Form factor
- 1/2U, fanless
- Capacity
- Up to 200 assets
- Setup
- Ships configured, plugs into the existing switch
- Data
- Stays on site

Large
Access Gate CMMC Performance
$14,235 per site, per year
It fits a main plant with more machines.
- Form factor
- 1U rack, server-grade
- Capacity
- Up to 1,000 assets
- Duty
- Continuous, in a plant cabinet
- Data
- Stays on site
Questions about CMMC on the shop floor.
to be up and running on your shop floor. The full CUI enclave is complete in a week.
It can, for CUI that stays on site. Access Gate covers the controls on premises, and whether you also need GCC High depends on your contract. If you already run GCC High or CUI Vault, the two work together. The cloud enclave holds CUI until it reaches your plant, and Access Gate protects it from there to the machines.
CMMC Level 2 requires all 110 controls of NIST SP 800-171 for contractors that handle CUI, under 32 CFR Part 170 and DFARS 252.204-7012. Contractors keep a System Security Plan (SSP) and a plan of action and milestones (POA&M). They post their score in SPRS, and a senior affirming official signs the affirmation. Access Gate covers the technical network controls on site: access, audit, identification and encryption.
A CMMC Level 2 checklist maps to the 110 NIST 800-171 controls across 14 families. They include access control, audit, identification and authentication, configuration management and communications protection. Access Gate enforces 87 of the 110 at the network layer and produces the evidence for each. The remaining 23 are customer-owned process controls, tracked in a Shared Responsibility Matrix.
Access Gate is installed in a day. You connect it to your existing firewall or router and add one rule that forwards the machine traffic to it. Removing that rule is the rollback. There is no re-cabling and no IP change. A single-plant CUI enclave is complete in a week, including scope, policies and evidence. With CUI Vault, the full setup from cloud enclave to machine is up in a week.
Access Gate provides enforcement evidence for 87 of the 110 NIST 800-171 controls. Coverage is strongest in access control, audit, configuration management, identification and authentication, and communications protection. The other 23, such as physical security and personnel screening, are customer-owned. The Shared Responsibility Matrix shows which controls Access Gate enforces, which it supports and which stay with you. Assessors can review access logs, policies and session recordings on demand.
Yes. Vendors log in with MFA and reach only the machines you allow, for a limited time. Every session is recorded. The link runs over the VPN built into Access Gate CMMC Edition, which uses a FIPS 140-3 validated cryptographic module.
A CUI enclave is an isolated part of your network that holds every system touching CUI: file servers, engineering workstations, printers and the shop-floor machines that receive drawings and toolpaths. Only the enclave is in scope for a CMMC Level 2 assessment. It can run on premise or extend a GCC High enclave such as CUI Vault down to your plant. See the CUI enclave architecture.
CMMC for a defense supplier usually comes in two parts: an IT enclave for the people who handle CUI, and Trout Access Gate for the machines that receive it. The IT enclave can be Microsoft GCC High through a managed provider such as Summit 7, CUI Vault or C3 Integrated Solutions, an encrypted email and file overlay such as PreVeil, a single hardened PC such as Totem, or a hosted virtual desktop such as Cuick Trac. Those enclaves end at the plant boundary. Trout Access Gate CMMC Edition sits beside the CNCs, PLCs and printers that receive CUI. It enforces 87 of the 110 NIST SP 800-171 controls at the network layer and produces the evidence for each. A registered practitioner or consultant handles the policies, the System Security Plan and the SPRS score. See CMMC enclaves for small manufacturers.
No. Connect Access Gate to your existing firewall or router, and add one rule that forwards the machine traffic to Access Gate. Removing that rule is the rollback. Nothing is installed on the machines.
Protect CUI on your shop-floor machines.
Tell us about your plant. We will map the path from your enclave to your machines and give you a fixed price before you commit.