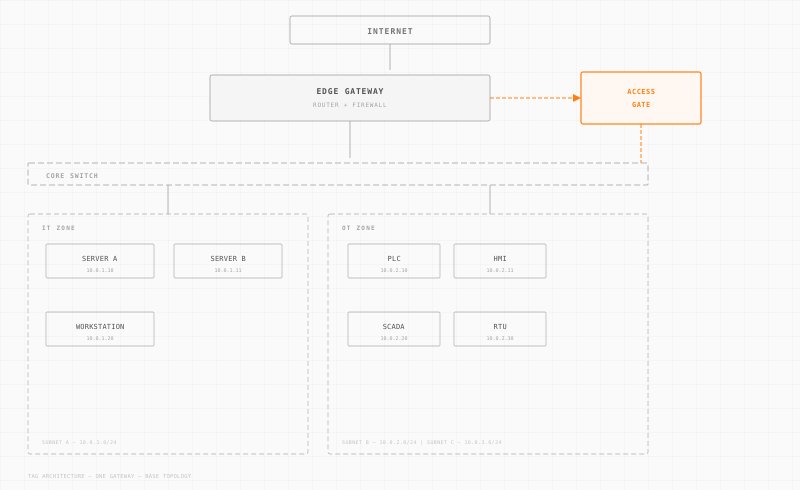
A specialized asset is a category defined in 32 CFR Part 170, the CMMC Program Rule, for equipment that processes, stores, or transmits Controlled Unclassified Information but cannot be fully configured to meet all 110 NIST SP 800-171 Rev 2 controls. The category matters because CMMC scopes the assessment differently for specialized assets than for general IT: at Level 2 they are documented in the System Security Plan rather than assessed against every requirement.
What counts as a specialized asset?
The CMMC rule names five asset types:
- Government-Furnished Equipment (GFE): hardware the customer provides that the contractor cannot reconfigure.
- Internet of Things (IoT): networked sensors, cameras, and embedded controllers with no general-purpose operating system.
- Operational Technology (OT): PLCs, DCS, SCADA, HMIs, CNCs, and industrial controllers running firmware.
- Restricted Information Systems: systems whose configuration is fixed by contract, export control, or security classification.
- Test Equipment: calibrated instruments, probes, and measurement systems where a firmware change invalidates the calibration.
How does CMMC assess specialized assets?
At Level 2, specialized assets must be documented in the asset inventory and the System Security Plan, and the assessor reviews that documentation; they are not assessed against the other CMMC requirements (32 CFR 170.19(c)). The plan should identify each one, the CUI that flows to or from it, and the compensating controls that protect it. At Level 3 they are assessed against all requirements, with intermediary devices allowed. See how CMMC handles exceptions and compensating controls for OT.
This is not a loophole. A specialized asset still has to be risk-managed; it just cannot be held to controls its firmware does not support. The contractor takes on the burden of proving risk equivalence at the network and process layers, and of producing evidence an assessor can inspect.
What do specialized asset scenarios look like?
- A CNC controller receives G-code files containing CUI technical drawings. It runs 10-year-old firmware with no TLS, no MFA, and no audit logs. It is a specialized OT asset. Compensating controls enforce identity, encryption, and logging at a network proxy in front of it.
- A calibrated pressure sensor on a munitions test stand transmits readings over serial and has no concept of authentication. It is specialized test equipment. Physical access control and network isolation are the compensating mechanisms.
- A government-furnished inspection camera sits on a segment that touches CUI data flows. Its firmware is owned by the customer. It is GFE, and the boundary drawn around it is the control.
Why do specialized assets matter for OT environments?
Because most defense manufacturing runs on exactly this kind of equipment: unpatchable controllers, decade-old firmware, and instruments that cannot be reconfigured without breaking calibration or warranty. The specialized-asset category is what lets a contractor keep that gear in production and still pass a CMMC assessment, provided the compensating controls at the OT security boundary are real and provable. The risk moves off the device and onto the network, which is where it can actually be managed.
Related terms
- CMMC Enduring Exception
- Compensating Control (CMMC)
- Operational Technology Security
- Controlled Unclassified Information
- Programmable Logic Controllers
How Access Gate helps
Access Gate protects specialized assets by enforcing identity, encryption, and audit at the network layer, producing C3PAO-ready evidence for equipment that cannot satisfy the controls itself. See CMMC Enduring Exceptions for OT.