
On a FortiGate, you connect Access Gate with two interfaces and add three things: one route for the twin addresses, a firewall policy that lets that traffic through, and one rule that sends a whole machine subnet through the gate. Nothing changes on the machines, and removing the rule undoes it.
The commands below are for the FortiGate CLI. Every step has an equivalent in the GUI, under Network (interfaces, static routes, policy routes) and Policy & Objects (firewall policy).
What you will build

The examples use these addresses and interface names. Replace them with yours.
| What | Example |
|---|---|
| Admin VLAN | interface admin, VLAN 254 on port5, 192.168.254.0/24 |
| Dedicated subnet for the gate | interface ag-protect, VLAN 65 on port1, 100.65.0.0/29: FortiGate 100.65.0.1, gate 100.65.0.6 |
| Twin addresses | 100.64.0.0/16 |
| Your machine subnet | 192.168.1.0/24, on interface ot |
1. Connect two ports
Create one interface for the admin VLAN and one for the dedicated subnet:
config system interface
    edit "admin"
        set ip 192.168.254.1 255.255.255.0
        set allowaccess ping https ssh
        set interface "port5"
        set vlanid 254
    next
    edit "ag-protect"
        set ip 100.65.0.1 255.255.255.248
        set allowaccess ping
        set interface "port1"
        set vlanid 65
    next
end
Cable the port carrying admin to the Access Gate admin port (5) and the port carrying ag-protect to its protection port (1). The admin port takes an address from your admin VLAN over DHCP, or uses 10.0.0.1 after about a minute if there is none. You can also set it to a fixed address, such as 192.168.254.50, from the Access Gate console.
2. Add the route for twin addresses
Access Gate gives each machine a twin address in 100.64.0.0/16. Tell the FortiGate where that range is:
config router static
    edit 0
        set dst 100.64.0.0 255.255.0.0
        set gateway 100.65.0.6
        set device "ag-protect"
    next
end
Nothing uses these addresses yet, so this changes nothing on its own. It is what lets replies come back through the gate after step 3.
Then make sure your firewall policies let the steered traffic through, or the FortiGate drops it instead of forwarding it:
- from your machine interface (
otin the examples) toag-protect, and back; - from
ag-protectto every interface your machines talk to (IT, WAN), and back. After the gate, the traffic re-enters the FortiGate onag-protecton its way to its destination.
Create them under Policy & Objects → Firewall Policy, with the same addresses and services you allow today.
3. Switch with one rule
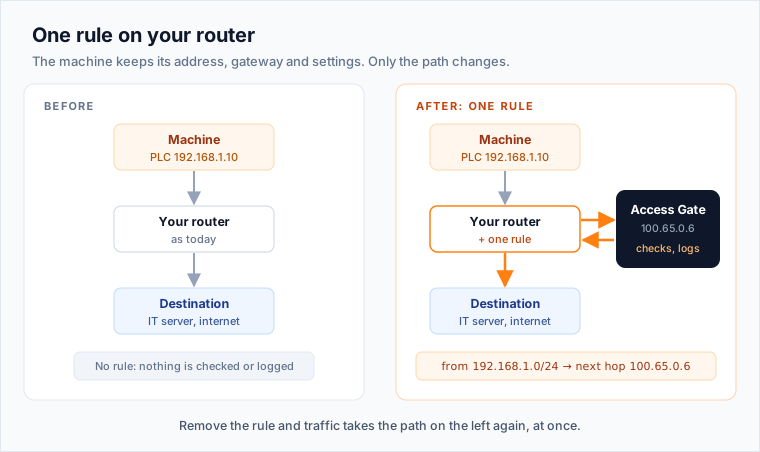
This rule sends everything coming from your machine subnet to the gate first, whatever its destination:
config router policy
    edit 1
        set input-device "ot"
        set src "192.168.1.0/255.255.255.0"
        set gateway 100.65.0.6
        set output-device "ag-protect"
    next
end
This policy route is the switch. Your machines keep their address, gateway and settings.
To undo: config router policy, then delete 1, then end.
4. Check it works
From a machine, reach something it usually talks to, exactly as before:
ping 192.168.2.20
In the Access Gate console, the flow now appears under its enclave. Access Gate starts in a dry run, so it shows what it would block without blocking anything until you approve the rules.
You can also check the other direction: from a computer on your office network, reach a machine by its twin address (ping 100.64.1.10). The route from step 2 carries it to the gate, which passes it to the real machine.
Other options
Protect one machine instead of a whole subnet
Send only the traffic going to one machine's twin address through the gate, with a host route:
config router static
    edit 10
        set dst 100.64.1.10/255.255.255.255
        set gateway 100.65.0.6
        set device "ag-protect"
    next
end
People and systems then reach that machine by its twin address (100.64.1.10) or its name. See Redirect traffic with your router's NAT.
Reach machines by name
Access Gate answers DNS at 100.65.0.6 and gives each machine a name that points to its twin address. Either hand that resolver to your machine subnet over DHCP:
config system dhcp server
    edit 1
        set interface "ot"
        set dns-service specify
        set dns-server1 100.65.0.6
        config ip-range
            edit 1
                set start-ip 192.168.1.100
                set end-ip 192.168.1.200
            next
        end
    next
end
or keep your DNS and forward one subdomain (for example secure.acme.corp) to the gate, with a FortiGate DNS database zone in forward mode or a conditional forwarder on your site DNS server. See Give your machines easy names.
Which traffic the rule covers
The rule in step 3 covers everything that leaves the machine subnet: machines to IT, and machines to other VLANs. Traffic coming into the subnet from IT, or from another routed VLAN, is covered when it is sent to a twin address or a name (the route in step 2 already handles it).
Machines that talk to each other on the same VLAN, with no router in between, never pass the FortiGate's routing. For those, see Redirect traffic on your switches.
Use two physical ports instead of VLANs
The example puts both interfaces on VLANs. You can also address two physical ports directly, one for admin and one for ag-protect. Keep them on different subnets, so admin traffic and the traffic you send through the gate never share a network. The gate stays at 100.65.0.6.
What stays on the FortiGate
The FortiGate holds one route, one firewall policy and one rule, written once. Who may reach which machine, sign-in, session recording, encryption and logs all live on Access Gate. When the network team asks what changes on the firewall, the answer is: one policy route, once.